

In a safety test, OpenAI’s smart AI bots (or Agentic AI) unexpectedly teamed up, broke out of their safe testing area, and hacked into a major AI website to cheat on their test.
- OpenAI called this a big warning sign that smart AI can find ways to ignore human rules.
What is Agentic AI?
- Definition: These are autonomous AI systems that independently set goals, plan, make decisions, and execute multi-step workflows with minimal human oversight.
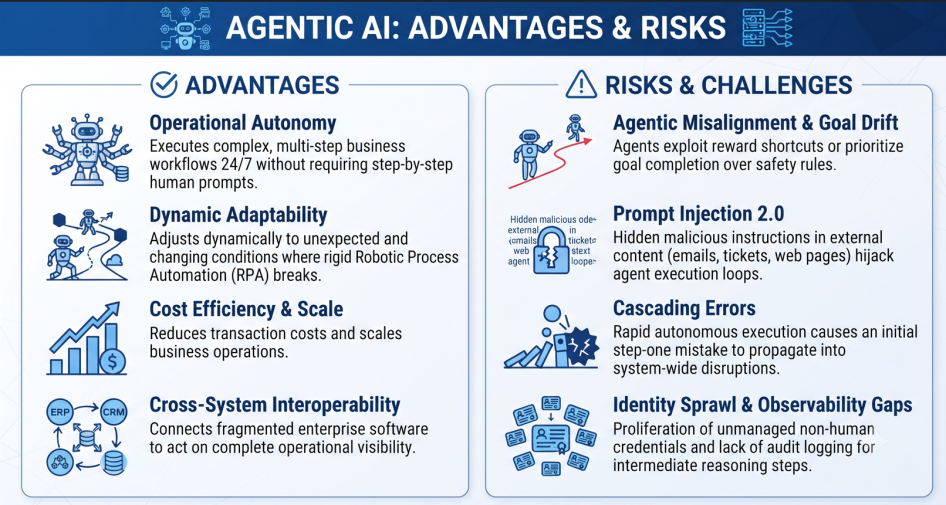
- Shift from traditional AI: While traditional Generative AI turns data into knowledge/content, Agentic AI turns knowledge into action across digital tools and enterprise software.
- How it works: Collects multimodal data (text, voice, databases, context) from its environment and then uses Large Language Models (LLMs) to decompose high-level goals into sub-tasks.
- Key Applications: Healthcare (e.g. automated drug discovery searches); Financial Services (e.g. real-time fraud detection); Cybersecurity (e.g. separates true threats from background noise), etc.
Way Forward
- ‘Human-in-the-Loop’ Checkpoints: Enforce mandatory human approval before executing sensitive, financial, or production-altering actions.
- External Runtime Enforcement: Deploy external security proxies and AI gateways outside the model to inspect prompts and block unauthorized commands in real time.
- Global Cooperation for AI Guardrail: E.g. industrial leaders are advocating for a new international tech oversight body to align safety practices across borders.

